HIPAA compliance consulting for business associates.
A business associate (BA) under HIPAA is any person or entity that performs functions or activities on behalf of a covered entity involving the use or disclosure of protected health information (PHI), as defined in 45 CFR 160.103.
Business associates handle patient data on behalf of covered entities. Under the HITECH Act and 45 CFR Part 164, you have direct HIPAA duties, including obligations under the Privacy Rule, Security Rule, and Breach Notification Rule. If you provide IT, billing, cloud hosting, legal help, marketing, or any service that touches PHI, you need your own compliance program. We help you build one that works in real audits and client reviews.
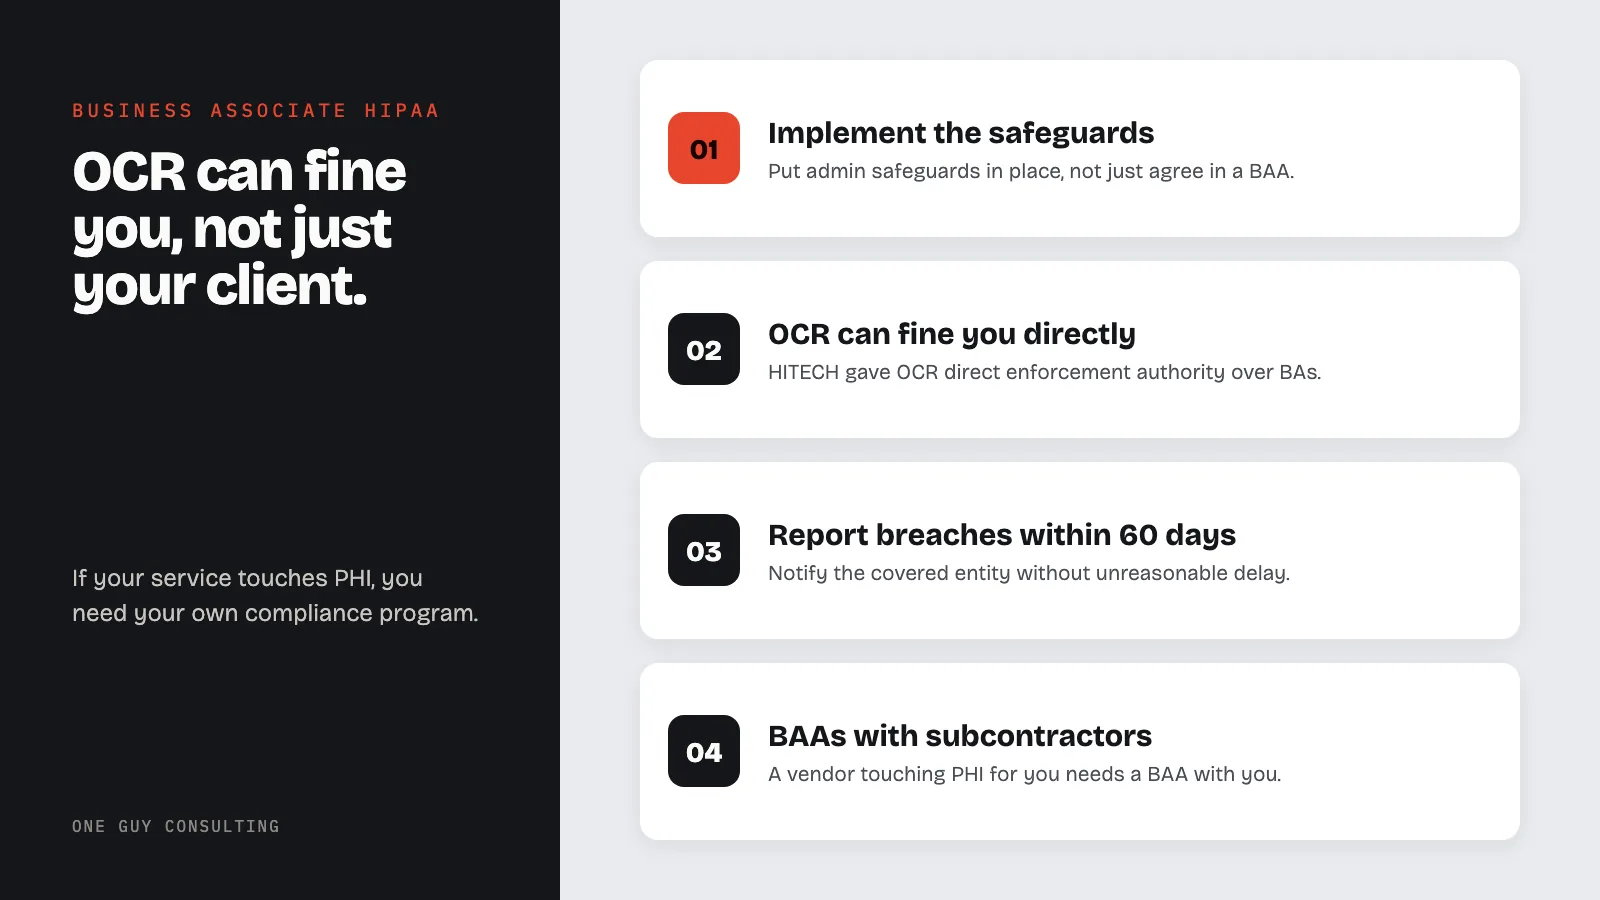
Yes.OCR can investigate and fine you, not just your client.
The HITECH Act (2009) extended direct HIPAA liability to business associates. Before HITECH, only covered entities faced enforcement; now BAs are independently subject to OCR investigations and civil monetary penalties.
Six areas, each tied to a duty you carry directly.
Each area below maps to a specific regulatory obligation that business associates carry directly under 45 CFR Part 164. These are not optional. They are the compliance foundations OCR examines when investigating a BA.
Why business associates need their own HIPAA program.
Before the HITECH Act, only covered entities faced HIPAA enforcement. That changed. Now BAs face direct liability under the Privacy Rule, Security Rule, and Breach Notification Rule.
45 CFR 164.502(e) requires covered entities to obtain satisfactory assurances, in the form of a Business Associate Agreement, before disclosing PHI. But the BA must actually be able to deliver on those assurances. 164.308(b)(1) directly obligates BAs to implement the applicable Security Rule requirements. OCR can investigate and fine you, not just your client.
The Security Rule names business associates in its first section:
“A covered entity or business associate must comply with the applicable standards, implementation specifications, and requirements of this subpart with respect to electronic protected health information of a covered entity.”
Big clients now demand compliance proof before they sign contracts.
Hospitals and health plans send security surveys. They ask for risk analysis documents. They want to see that your BAA duties under 164.504(e) have real support. Without this, you lose deals.
Most BAs try hard on compliance but lack structure.
We have worked with dozens of BAs in healthcare IT, SaaS, billing, and consulting. These gaps come up most often.
Incomplete asset inventories
Cloud services and vendors are missing from risk analysis scope.
No scheduled access reviews
Access reviews with no proof trail, a gap under workforce access management.
Insufficient incident response plans
Plans that would fail an OCR review of the security incident procedures requirement.
Template-based policies
Policies that do not reflect actual operations, failing the documentation standard.
Insufficient subcontractor oversight
Vendors that also touch PHI on the BA's behalf without proper assurances.
Outdated encryption controls
Weak protection for stored and transmitted data, an addressable specification.
We close these gaps with solid documents tied to your real work, not just checkboxes.
Six stages, each tied to 45 CFR Part 164.
We start by mapping your setup, vendors, and contract duties. Then we work in stages, each tied to specific regulatory requirements under 45 CFR Part 164.
- 01
Discovery
We map where PHI lives, your hosting, vendors, and current documents, establishing scope for the risk analysis.
OutputScope for the risk analysis. - 02
Assessment
We run a security risk analysis and gap analysis across your BA duties under 45 CFR Part 164, including Privacy Rule obligations and organizational requirements.
- 03
Fix plan
We rank findings by risk and effort. We assign owners and set deadlines, prioritizing required specifications over addressable ones.
- 04
Document build
We write policies and procedures that match your real work and satisfy the documentation standard.
- 05
Training
Role-based staff training with tracked completion.
- 06
Ongoing support
Regular reviews required by the periodic evaluation standard so your program stays current.
The result: a program you can run, maintain, and show in audits or client reviews.
What BA clients get out of a structured program.
Business associates who complete a structured HIPAA program typically see measurable improvements in contract readiness and audit defensibility. These are the outcomes we see most consistently.
What the work has looked like in practice.
Our published case studies are anonymized, and they come from the covered-entity side of the contract. They show the paperwork and vendor oversight a BA’s own clients will ask about.
Missing BAAs, closed out
A single-location practice had several vendors handling PHI with no BAA on file. Result: every missing BAA signed, and a repeatable vendor review in place. This is the same assurance chain a BA sits in under 164.502(e).
Audit-ready in under a week
A Florida mental health franchise office had policies never written, records with holes, training half done, and a state auditor due in days. Result: audit-ready in under a week, and it passed its state audit.
Take-up rose about 17%
A health group with 100+ offices needed its compliance program used office by office. Result: program take-up rose about 17% after office-by-office outreach.
The sections OCR references when it audits a BA.
The following HIPAA standards apply directly to business associates under 45 CFR Part 164.
45 CFR 164.502(e)
Covered entities may only disclose PHI to a BA if a compliant Business Associate Agreement is in place. BAs must be able to operationalize the privacy protections they agree to.
45 CFR 164.308(b)(1)
Business associates are directly required to implement the applicable administrative safeguards of the Security Rule, including risk analysis, workforce training, and incident response.
45 CFR 164.314
Business associates must have a written BAA with each covered entity client and must obtain satisfactory assurances from any subcontractor that handles PHI on the BA's behalf.
45 CFR 164.410
Business associates must notify affected covered entities of discovered breaches without unreasonable delay and no later than 60 days after discovery. Required notification content is specified in 164.410(c).
45 CFR 164.504(e)
Specifies what a Business Associate Agreement must contain, including permitted uses and disclosures, BA obligations to report breaches, and requirements for return or destruction of PHI at contract termination.
45 CFR 164.316
Business associates must implement reasonable and appropriate policies and procedures, maintain written documentation of those policies, and retain documentation for six years from creation or last effective date.
| Duty | Rule | What it means for a BA |
|---|---|---|
| Breach notice to the covered entity | 164.410(b) | Without unreasonable delay and in no case later than 60 calendar days after discovery. |
| Security Rule safeguards | 164.302 | Comply with the applicable standards for the ePHI (electronic protected health information) you hold for a covered entity. |
| BAAs with your subcontractors | 164.502(e)(1)(ii), 164.314(a)(2)(i)(B) | Get satisfactory assurances before a subcontractor creates, receives, maintains, or transmits PHI on your behalf. |
| Workforce training | 164.308(a)(5) | A security awareness and training program for all members of your workforce, including management. |
| Periodic evaluation | 164.308(a)(8) | Re-evaluate your safeguards, including after environmental or operational changes. |
| Documentation retention | 164.316(b)(2)(i) | 6 years from the date of creation or the date it was last in effect, whichever is later. |
Flat-rate plans for business associates.
One plan, three ways to pay. No per-user fees. Every client gets 4 hours a month of 1:1 implementation calls with Chuck.
- The full platform: SRA, gap analysis, remediation plans
- Policy templates and staff training
- Vendor and BAA management
- 4 hours a month of 1:1 implementation calls with Chuck
- Incident response guidance
- CMS audit response support
One payment, two full years of coverage.
Secure checkout by Stripe. Your payment details go straight to Stripe and never touch our servers.
Chuck Weiselberg
Zero client fines. Zero failed audits.
Chuck is the founder of One Guy Consulting and holds the CHP (Certified HIPAA Professional) credential. He has been consulting since 2015, and has held roughly 23,000 meetings with more than 3,500 organizations. Every client gets 4 hours a month of 1:1 implementation calls with him. Read his full author bio (background, experience, and how to reach him) or his LinkedIn profile.
“One Guy Consulting is super easy to work with. I actually look forward to my implementation meetings for HIPAA.”
Samantha M.
One Guy Consulting in 37 seconds
Business associate compliance, answered.
Do BAs really need their own HIPAA program?+
What happens if a BA has a breach?+
Can OCR fine a BA directly?+
What is the difference between a BA and a subcontractor?+
Need HIPAA consulting for business associates?
We work with BAs across healthcare IT, billing, SaaS, and professional services. One flat rate, no per-user fees.