HIPAA Compliance Plans
Full-Scope is $1,300 a year, or $120 a month: one flat rate per location, with no per-user fees and no add-on charges. Pay monthly, every 12 months, or every 24 months ($2,300). HIPAA compliance is complicated enough. Pricing doesn't have to be.
Curious what the work actually looks like? See the HIPAA compliance process step by step.
Small practices typically budget $5,000 to $15,000 for HIPAA compliance consulting (source: Medcurity, 2026). Full-Scope is $1,300 a year, flat.
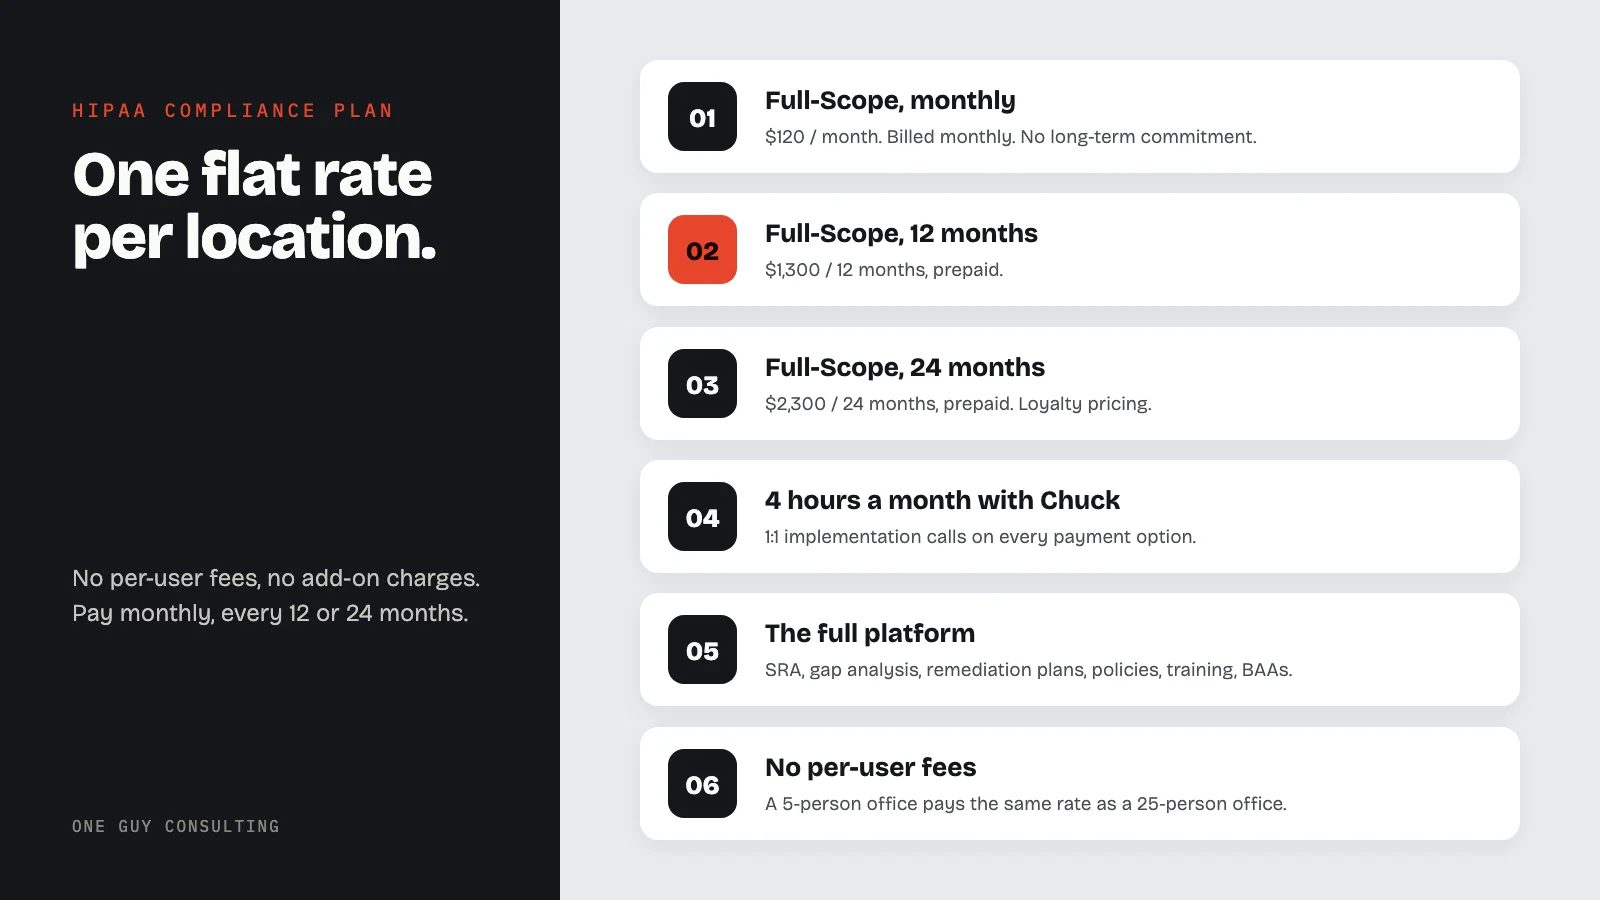
Prepaid annually. 2-year loyalty pricing available.
For a breakdown of pricing in greater detail, please visit our pricing breakdown page.
The full compliance platform, plus 1:1 help from Chuck:
- Security Risk Assessment
- Gap Analysis & Remediation Plans
- Policy & Procedure Templates
- Staff Training & Progress Tracking
- IT & Physical Site Audits
- Vendor Management & Digital BAAs
- Incident Management System
- 4 hours a month of 1:1 implementation calls with Chuck
- Personalized Implementation
- Incident Response Guidance
- CMS Audit Response Support
Flat rate per location. 90-day money-back guarantee: not a fit in the first 90 days, you get a full refund. Monthly plans have no long-term commitment. We never ask for patient information.
Secure checkout by Stripe. Your payment details go straight to Stripe and never touch our servers.
Want to check one office computer first? A one-time vulnerability scan, $59.
What the Full-Scope Plan Includes
| Feature | Full-Scope |
|---|---|
| Security Risk Assessment | ✓ |
| Gap Analysis & Remediation Plans | ✓ |
| Policy & Procedure Templates | ✓ |
| Staff Training (HIPAA 101, CyberSecurity, Policy Attestation, FWA, Bloodborne Pathogen, Sexual Harassment) | ✓ |
| Training Progress Tracking & Reminders | ✓ |
| IT Inventory, Network & Physical Site Audits | ✓ |
| Vendor Management & Digital BAA Execution | ✓ |
| Incident Management & Anonymous Reporting | ✓ |
| Plus, 1:1 with Chuck | |
| 4 Hours a Month of 1:1 Personalized Implementation | ✓ |
| Incident Response Guidance | ✓ |
| CMS Audit Response Support | ✓ |
What Full-Scope Work Has Looked Like for Real Practices
A price only matters if the work holds up. Here are three examples from my case studies, with client names left out to protect their privacy.
A franchise office had policies that were never written, records with holes, and staff training half done, with a state auditor due in days. It was audit-ready in under a week and passed its state audit. Read case 01
A single-location practice had several vendors handling PHI (protected health information) with no BAA (business associate agreement) in place. Every missing BAA got signed, and the practice came away with a repeatable vendor review. Read case 05
A health group with more than 100 offices needed more of its offices to take up its compliance program. After office-by-office outreach, program take-up rose about 17%. Read case 03
Chuck Weiselberg is the founder and HIPAA consultant behind One Guy Consulting and a Certified HIPAA Professional (CHP), consulting since 2015. Across his career he has logged roughly 23,000 meetings with more than 3,500 organizations. Zero clients fined. Zero failed audits. Every Full-Scope plan includes 4 hours a month of 1:1 implementation calls with him. Read his full author bio.
One Guy Consulting in 37 Seconds
HIPAA Compliance Definitions
These terms appear throughout the HIPAA rules and in every OGC workflow. They help clarify which requirements each service addresses.
Security Risk Assessment (SRA)
A review of threats and weak points in how you protect electronic health data (ePHI). Required under 45 CFR § 164.308(a)(1), the SRA is the base of every HIPAA program and the first item OCR asks for in an audit.
Protected Health Information (PHI)
Any health data tied to a specific person, including medical records, billing data, and insurance details, that is created, received, stored, or sent by a covered entity or business associate. When it is in digital form, it is called ePHI.
Business Associate Agreement (BAA)
A required written contract between a covered entity and any vendor that touches PHI on its behalf. The BAA spells out allowed uses of PHI, required safeguards, and breach notice duties under 45 CFR § 164.502(e).
Gap Analysis
Built from your SRA answers, organized by the HIPAA Security Rule (45 CFR Part 164, Subpart C) and Privacy Rule (Subpart E). Shows what is strong, what is missing, and what poses the most risk if left unfixed.
What Each Service Covers and Why It Matters
Every service and tool seen online is in the Full-Scope plan here at One Guy Consulting. They each have a purpose, and most tie to a HIPAA regulation specification. Below you will find what each service covers and its purpose. That way, you can check your audit readiness.
The first item on the list, in the regulation’s own words:
Conduct an accurate and thorough assessment of the potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic protected health information held by the covered entity or business associate.45 CFR 164.308(a)(1)(ii)(A), Risk analysis (Required)
- 01
Security Risk Assessment
Guided risk analysis through the OGC portal. It finds threats, weak points, and current safeguards. Then it builds your documented risk analysis, required under 45 CFR §164.308(a)(1)(ii)(A).
- 02
Gap Analysis & Remediation Plans
Built from your SRA results. It compares your current controls to Security Rule and Privacy Rule standards, finds gaps, and creates a ranked fix plan. You will know what to fix and in what order. Under 45 CFR §164.308(a)(1)(ii)(B), covered entities must reduce risks and weak points. The fix plan is your proof of meeting this rule.
- 03
Policy & Procedure Templates
HIPAA policies covering the Privacy Rule, Security Rule, and Breach Notification Rule. Each policy is shaped to your org's size, type, and workflow, then posted to your branded portal. Written policies are required under 45 CFR §164.316. They must be kept for six years from the date they were created or last in effect, whichever is later.
- 04
Staff Training & Progress Tracking
Role-based training with progress tracking and sign-off records. HIPAA 101, Cybersecurity and Policy Attestation cover HIPAA's training rules: the Security Rule training program (45 CFR §164.308(a)(5)) and Privacy Rule training (45 CFR §164.530(b)). FWA, Bloodborne Pathogen and Sexual Harassment are extra modules outside HIPAA.
- 05
Vendor Management & Digital BAAs
Vendor list with risk ratings, BAA creation and tracking, and due diligence records for each vendor. Meets the business associate contract rule under 45 CFR § 164.502(e).
- 06
Incident Management & Anonymous Reporting
Tools to log, review, and respond to security events and possible breaches. Supports the Breach Notification Rule (45 CFR §§ 164.400 to 414). Affected individuals must be notified without unreasonable delay and no later than 60 days after a breach of unsecured PHI is discovered. HHS is notified at the same time for breaches affecting 500 or more people; smaller breaches go in a log reported to HHS within 60 days after the end of the calendar year.
Frequently Asked Questions
Common questions about HIPAA costs, rules, and what the plan includes.
What HIPAA requirements drive the cost of compliance?+
Is a Security Risk Assessment required every year?+
Why do HIPAA compliance costs vary so much between vendors?+
What happens if a covered entity does not have a Business Associate Agreement with a vendor?+
Does HIPAA require staff training, and what must it cover?+
Talk it through with Chuck first.
A free 30-minute intro call covers where your program stands and whether Full-Scope makes sense for your size.