By Chuck Weiselberg, Founder, One Guy Consulting. Published .
Chuck Weiselberg, Founder at One Guy Consulting: specializes in HIPAA compliance for healthcare practices. Certified HIPAA Professional (CHP), 10 years of HIPAA compliance experience. Full author bio
This guide explains the HIPAA compliance essentials for optometry practices and next steps to reduce risk with One Guy Consulting's support.
HIPAA (the federal law protecting health information) compliance for an optometry practice means protecting patient records in the clinic and the optical shop as one system. It takes a risk assessment, written policies, staff training, and an incident procedure. You also need business associate agreements (BAAs) with vendors that handle patient data. Nearly every practice must follow HIPAA, because filing vision plan claims electronically is enough.
An optometry practice is two businesses sharing one front door. On one side: a clinical operation with exams, diagnoses, dilations, and electronic insurance claims. On the other: a retail store selling frames, lenses, and contacts to anyone who walks in. The two sides share a computer system, a front desk, and a staff, and that sharing is where optometry's HIPAA problems actually live.
This article covers the covered-entity question, where the clinic-retail line runs through your data, which labs and suppliers need a BAA, and the front-of-house practices that matter when your waiting room is also a showroom.
What HIPAA means for optometry practices
HIPAA compliance for optometry comes down to three questions: who the rules apply to, what information they protect, and when the deadlines run. HHS OCR (the federal HIPAA enforcement office in the U.S. Department of Health and Human Services, also called OCR) enforces them; its HHS OCR HIPAA guidance and the American Optometric Association (AOA) HIPAA resources are the two references worth bookmarking.
Who: You Are Almost Certainly a Covered Entity
The test is electronic standard transactions: file claims to vision plans or medical insurance electronically, check eligibility, receive electronic remittance, and you are a covered entity under HIPAA (45 CFR 160.103). For optometry, that is nearly everyone: optometrists (doctors of optometry licensed to examine eyes and prescribe lenses) bill vision plans and medical insurance electronically every day. Filing vision plan claims electronically is enough on its own. The full test lives in the covered entity guide, but optometry rarely needs the nuance: if you bill VSP-style plans electronically, or bill medical insurance electronically for eye disease visits, you are in.
What: What Counts as PHI in an Optometry Practice
The exam record, obviously. But also: the spectacle and contact lens prescriptions, the optical order tied to a patient name, vision plan claims and authorizations, referral letters to ophthalmology, retinal images and OCT scans, and the recall list your reminder system runs on. The instinct to treat "the shop side" as retail data fails in practice, because the frame order references the Rx, the Rx references the exam, and it all lives in one practice-management system. The workable rule: protect the whole system as if everything in it is PHI (protected health information), because functionally it is.
When: The Deadlines That Apply
- 30 days to act on a patient's request for their records, with one 30-day extension (45 CFR 164.524(b)(2)).
- 60 days at most after discovering a breach to notify affected patients (45 CFR 164.404(b)); a breach of 500 or more people is reported to HHS at the same time (164.408). See the OCR breach notification guidance.
- 6 years to keep HIPAA policies, training records and other required documentation (45 CFR 164.316(b)(2)(i)).
Practical steps: risk assessments, policies, and staff training
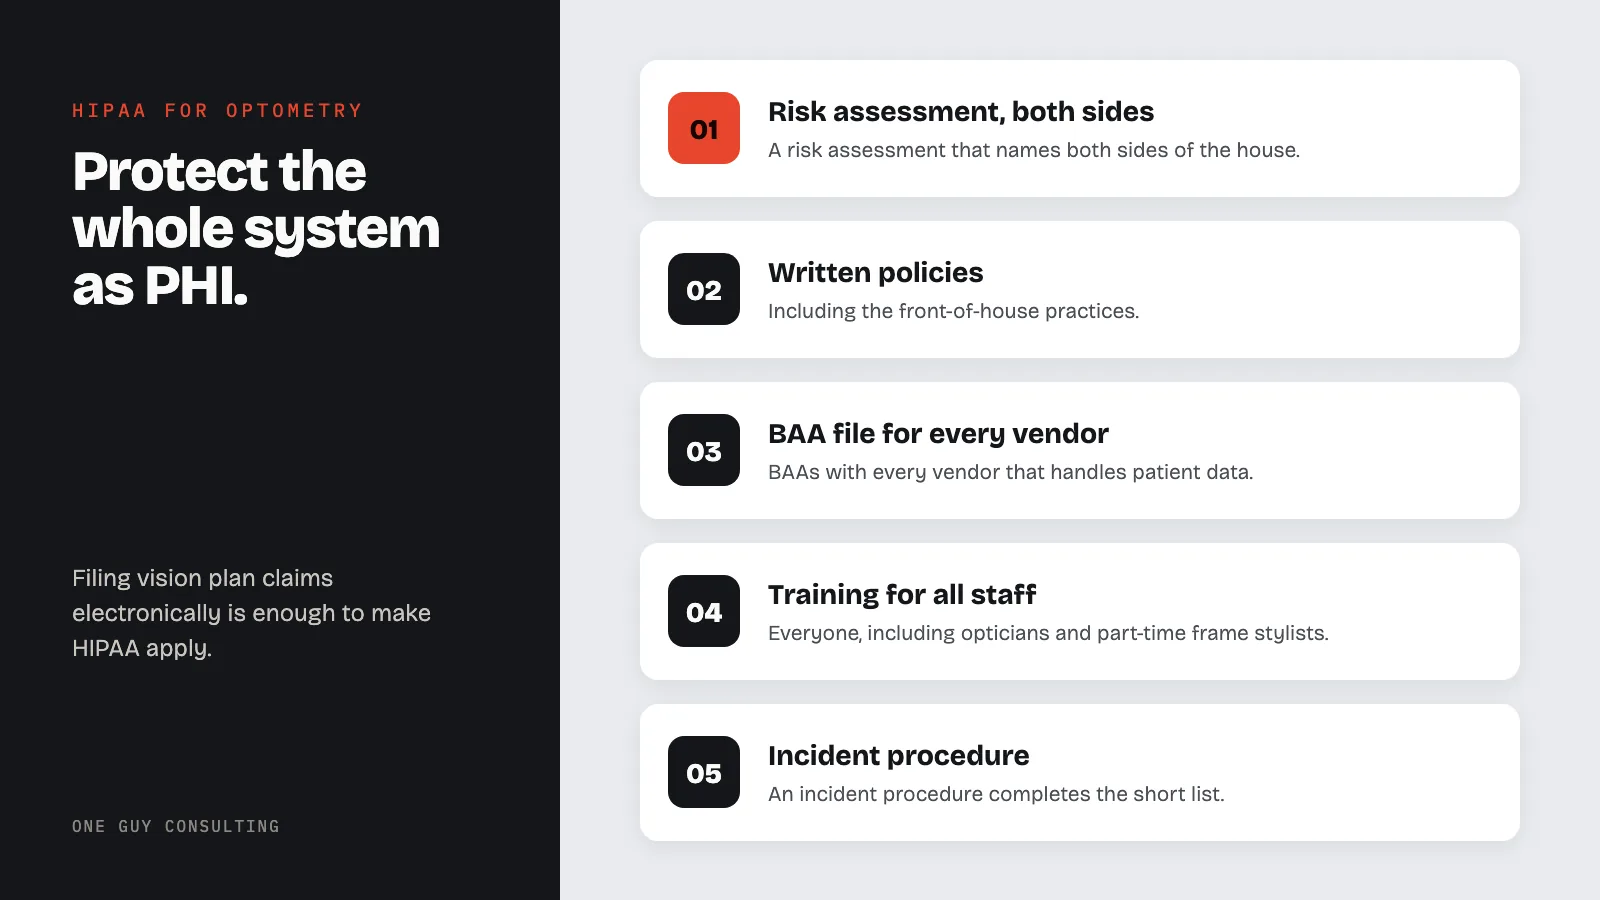
The baseline set: a risk assessment (a documented review that identifies threats to patient data, required by 45 CFR 164.308(a)(1)(ii)(A)) that names both sides of the house, written policies including the front-of-house practices, the BAA file with every vendor that handles patient data (plus any labs you choose to sign with), staff training for everyone including opticians and part-time frame stylists, and an incident procedure. It is a short list.
- Risk assessment: cover the exam lanes, the optical shop, the practice-management system, imaging devices and every laptop or phone that opens patient records.
- Policies: privacy, security, breach response and the front-desk rules, in writing (164.316(b)(1)).
- Training: every workforce member, with a written record of who was trained and when (164.530(b)). Practical topics are in HIPAA policies and training for small practices.
- Incident procedure: who to tell, how to assess whether it is a breach, and the 60-day clock above.
Technical safeguards and vendor (BAA) considerations
The HIPAA Security Rule's technical safeguards (45 CFR 164.312) apply to the practice-management system, the EHR and the imaging devices alike:
- Access controls (limit PHI access to the people who need it): a unique login for every doctor, tech and optician, and no shared front-desk account.
- Encryption (protect stored and transmitted data so only key holders can read it): laptops, backups and any email that carries prescriptions or exam results.
- Audit controls (a record of who opened which record): turned on in the EHR and practice-management system.
Business Associates and BAAs
A BAA (business associate agreement) is a contract HIPAA requires with any business associate (vendors handling PHI on your behalf) (45 CFR 164.504(e)). The BAA guide covers what goes in one. In optometry, the clear cases are the claims clearinghouse, the practice-management and EHR (electronic health record) vendor, and the recall/reminder platform. Each one holds patient data to work for you. So each needs a signed BAA before patient data flows.
Optical labs and contact lens fulfillment services are a gray area, even though every job you send a lab carries a patient name and prescription. HIPAA has an exception for health care providers. A provider that gets patient information to treat the patient is not a business associate (45 CFR 160.103).
A lab or supplier filling a prescription may fit that exception. If you are not sure which side a lab is on, asking it to sign a BAA is the cautious choice. A frame vendor you order inventory from with no patient information attached is not a business associate at all. Run the inventory once, then keep it current through vendor management.
A Waiting Room That Is Also a Showroom
Optometry's front desk sits in the middle of a retail floor. Browsers try on frames a few feet from where a tech collects an insurance card and a medical history. The rules here are the ordinary reasonable-safeguard rules (take reasonable steps so others do not see or overhear patient information), applied to an unusual floor plan: check-in conversations at a lowered voice, monitors angled away from the frame displays, dilation and diagnosis conversations in the exam lane rather than at the register, and pickup calls that say the glasses are ready without narrating the prescription. The complete front-of-house set is in the front desk rules.
Contact Lens Releases and Records Requests
Two patient-rights notes specific to this specialty. Federal law already requires releasing the contact lens prescription after fitting; HIPAA's right of access sits alongside it, giving patients their full record within 30 days for a cost-based fee. Requests from a patient's new eye doctor are treatment disclosures and need no authorization at all. Do not make patients fight for prescriptions they are entitled to; it invites a complaint.
How One Guy Consulting helps optometry offices
One Guy Consulting builds compliance programs for exactly this kind of hybrid: clinical obligations, retail floor, small team wearing both hats. The Full-Scope plan is $1,300 a year, or $120 a month, flat rate per location. It includes the risk assessment, policy templates, staff training, vendor management with digital BAAs, and 4 hours a month of 1:1 implementation calls with Chuck. Start with a free 30-minute call. No obligation, no pressure.
"One Guy Consulting helps optometry practices manage HIPAA risk and maintain patient privacy."
(One Guy Consulting)
Case example (anonymized; not an optometry practice): Before: several vendors touching PHI with no BAA in place. After: every missing BAA signed and a vendor review the practice can run again. Read case 05, or contact One Guy Consulting for details.
FAQ and next steps
What does this page cover?
HIPAA compliance topics tailored for optometry practices and how One Guy Consulting helps manage them.
Who should read this page?
Practice managers, office managers, and clinicians at optometry offices looking to meet HIPAA obligations.
What next steps should an optometry practice take?
Perform a HIPAA risk assessment, document policies, train staff, and contact One Guy Consulting for ongoing support.
Sources
- 45 CFR 160.103 (covered entity definitions)
- 45 CFR 164.524 (right of access)
- FTC Contact Lens Rule
- HHS OCR: HIPAA for professionals
- HHS OCR: Breach Notification Rule
- American Optometric Association: HIPAA compliance resources
- 45 CFR 164.312 (technical safeguards)
- 45 CFR 164.316 (documentation and retention)
Related Reading
Try three One Guy Consulting 3D staff training courses free →