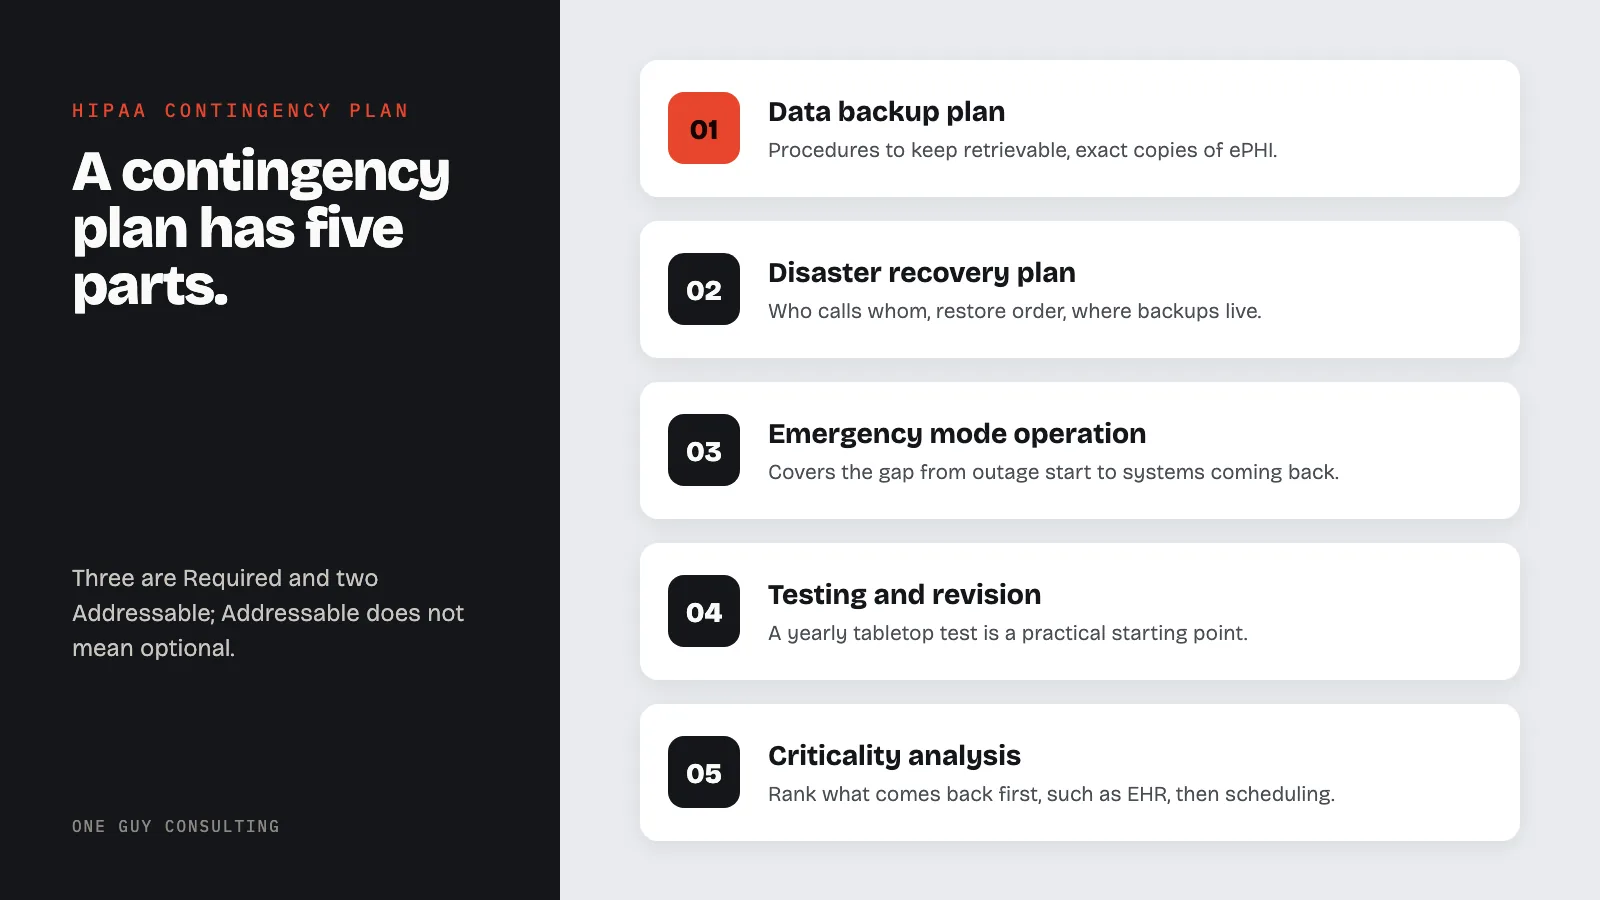
A HIPAA contingency plan is your written plan for keeping ePHI (electronic protected health information) safe and usable when systems fail. Under 45 CFR 164.308(a)(7), it has five parts. Three are Required: data backup, disaster recovery, and emergency mode operation plans. Two are Addressable: testing and revision, and applications and data criticality analysis. That does not mean optional.
Every practice finds out whether it has a contingency plan. The only question is whether the discovery happens during a calm Tuesday policy review or at 7:40 on a Monday morning when the EHR (electronic health record) will not load and the practice manager is staring at a ransom note.
The Security Rule assumed this day would come. 45 CFR 164.308(a)(7) requires every covered entity and business associate to "establish (and implement as needed) policies and procedures for responding to an emergency or other occurrence (for example, fire, vandalism, system failure, and natural disaster) that damages systems that contain electronic protected health information."
That standard comes with five implementation specifications. Three are Required. Two are labeled Addressable, and if you have read why addressable does not mean optional, you already know that label is not a permission slip.
What a HIPAA Contingency Plan Must Contain
Here is the regulation text for all five, word for word:
(A) Data backup plan (Required). Establish and implement procedures to create and maintain retrievable exact copies of electronic protected health information.
(B) Disaster recovery plan (Required). Establish (and implement as needed) procedures to restore any loss of data.
(C) Emergency mode operation plan (Required). Establish (and implement as needed) procedures to enable continuation of critical business processes for protection of the security of electronic protected health information while operating in emergency mode.
(D) Testing and revision procedures (Addressable). Implement procedures for periodic testing and revision of contingency plans.
(E) Applications and data criticality analysis (Addressable). Assess the relative criticality of specific applications and data in support of other contingency plan components.
1. Data Backup Plan (Required)
The rule asks for procedures to "create and maintain retrievable exact copies" of ePHI (electronic protected health information). Two words carry the weight: retrievable and exact. A backup you have never restored is a hope, not a plan. The test is simple: pick a file, restore it, time it, write down the result. If your EHR is cloud-hosted, your piece of this is knowing what the vendor backs up, how often, and how you would get your data out. "The vendor handles it" is an answer only if you can say what the vendor actually does.
2. Disaster Recovery Plan (Required)
Procedures to "restore any loss of data." This is the sequence document: who calls whom, in what order systems come back, where the backups live, and what the passwords situation is when the password manager is on the dead server. For a five-person office it fits on two pages. The two pages need to exist on paper, because the plan stored only on the system that just died is a joke that writes itself.
3. Emergency Mode Operation Plan (Required)
The least understood piece. It covers the gap between the outage starting and systems coming back: how do you keep treating patients, and how do you keep ePHI secure, while running on paper and phones? Downtime forms, a paper schedule pulled each morning, and a rule for where downtime notes go when the EHR returns. Security does not pause during the outage; that is the entire point of the specification.
4. Testing and Revision (Addressable)
The rule does not say how often to test. For a small practice, a tabletop test once a year is a practical starting point: sit down for one hour, walk through "the server is dead," find the three things that do not work, fix them, and document that you did. If you choose not to test, the Security Rule requires you to document why testing was not reasonable and what you did instead. Writing that memo honestly is usually harder than running the test.
5. Applications and Data Criticality Analysis (Addressable)
Rank what comes back first. EHR, then scheduling, then billing, then email is a common small-practice order, but yours depends on how you actually run. This is a one-hour worksheet, and it makes the disaster recovery plan honest: restoration order is a decision you make now, not an argument you have during the outage.
The Cloud Did Not Repeal This Rule
Moving to cloud systems changes the failure modes. It does not remove them, and it does not transfer your obligation. A cloud outage takes your practice offline just as thoroughly as a dead server, as the February 2026 Cloudflare outage showed businesses across every sector at once. Your vendor's promise to stay online is in their contract. It is usually called the SLA (service level agreement). Your contingency plan is what your office does during the hours those promises are being broken.
I start that conversation with the vendor list. At a single-location practice I worked with, several vendors were handling PHI (protected health information) with no BAA (business associate agreement) in place. We got every missing BAA signed and set up a vendor review the practice can repeat. I use that same review to ask each vendor the backup questions above: what it copies, how often, and how you get your data back out.
What OCR Asks For
After a ransomware incident or a breach report, OCR may investigate whether you follow the Security Rule. OCR is the HHS Office for Civil Rights, which enforces HIPAA. Section 164.308(a)(7) is part of that rule. Expect to produce the contingency plan and the written documentation behind it, which 164.316(b) requires you to keep for six years.
The six years count from the date it was created or the date it was last in effect, whichever is later. You can have your risk analysis and training logs ready and still get stuck here, because the plan was never written. It is a required standard, and its absence is a finding all by itself, separate from whatever caused the breach. The rest of the Security Rule picture is in the Security Rule implementation guide.
Missing paperwork can be fixed faster than most offices expect. In a Florida mental health franchise office I worked with, the policies had never been written, the records had holes, training was half done, and a state auditor was due in days. We got the office audit-ready in under a week, and it passed its state audit. I would not wait for an auditor to start a contingency plan, but I have seen a written program come together in days.
Build It in an Afternoon
One page per component, five pages total, most of it bullet points. Here is how I lay out the five pages:
| Page | Specification | Label | What goes on the page |
|---|---|---|---|
| 1 | Data backup plan (164.308(a)(7)(ii)(A)) | Required | What is backed up, how often, where the copies live, and the date of your last test restore |
| 2 | Disaster recovery plan (164.308(a)(7)(ii)(B)) | Required | Who calls whom, the order systems come back, and how to reach the backups and passwords |
| 3 | Emergency mode operation plan (164.308(a)(7)(ii)(C)) | Required | Downtime forms, the paper schedule, and where downtime notes go when the EHR returns |
| 4 | Testing and revision (164.308(a)(7)(ii)(D)) | Addressable | The annual tabletop test, what broke, what you fixed, or a written reason you chose another approach |
| 5 | Applications and data criticality analysis (164.308(a)(7)(ii)(E)) | Addressable | Your restoration order, ranked |
The policy template library gives you policy and procedure templates to start from. Fill in your plan, print two copies, put one somewhere that is not the server room, and calendar the annual test. That is the whole assignment.
FAQ
Is a contingency plan required for small practices?
Yes. 45 CFR 164.308(a)(7) applies to every covered entity and business associate regardless of size. Data backup, disaster recovery, and emergency mode operation plans are all designated Required.
Is cloud backup enough to satisfy HIPAA?
Cloud backup can satisfy the data backup specification if the copies are exact, retrievable, and you have verified restoration. You still need the disaster recovery and emergency mode pieces, which cover your office's response, not the vendor's.
How often should we test the contingency plan?
Testing is an addressable specification. The rule does not say how often to test. For a small practice, a yearly tabletop walkthrough that you write down is a practical starting point. If you decide not to test, write down why and what you will do instead.
What is an emergency mode operation plan?
The procedures for continuing critical business processes, and keeping ePHI secure, while systems are down: downtime forms, paper schedules, and how downtime documentation gets entered once systems return.
Do business associates need contingency plans too?
Yes. The Security Rule applies to business associates directly, and 164.308 names them explicitly. If you are a vendor holding ePHI, this is your obligation, not just your client's.
A contingency plan for a small practice is a short document, not a binder. One Guy Consulting's Full-Scope plan includes policy and procedure templates and 4 hours a month of 1:1 implementation calls with Chuck. Start with a free 30-minute intro call. No obligation, no pressure.
One Guy Consulting in 37 seconds
Sources
- 45 CFR 164.308 (administrative safeguards)
- 45 CFR 164.316 (documentation and the six-year retention rule)
- HHS Security Rule guidance material
- NIST SP 800-34: Contingency Planning Guide
Related Reading
- Addressable does not mean optional
- HIPAA Security Rule implementation
- The February 2026 Cloudflare outage and business lessons
Related reading: Cyber Insurance and HIPAA: Useful, but No Substitute for Risk Analysis
Try three One Guy Consulting 3D staff training courses free →