By Chuck Weiselberg, One Guy Consulting. Published .
Chuck Weiselberg, Founder and Certified HIPAA Professional (CHP), One Guy Consulting; 10 years of HIPAA compliance experience. Full author bio and contact
Building a healthcare compliance culture means making HIPAA (the US law protecting patient health information) part of how a practice works every day, not a binder on a shelf. A compliance culture (the shared habits a team uses to protect PHI, protected health information) rests on leadership and governance, staff training and routines, written policies and BAAs, and ongoing monitoring. The HHS Office for Civil Rights (OCR) enforces HIPAA; CMS and NIST publish the guidance that fills in the how.
Why compliance culture matters
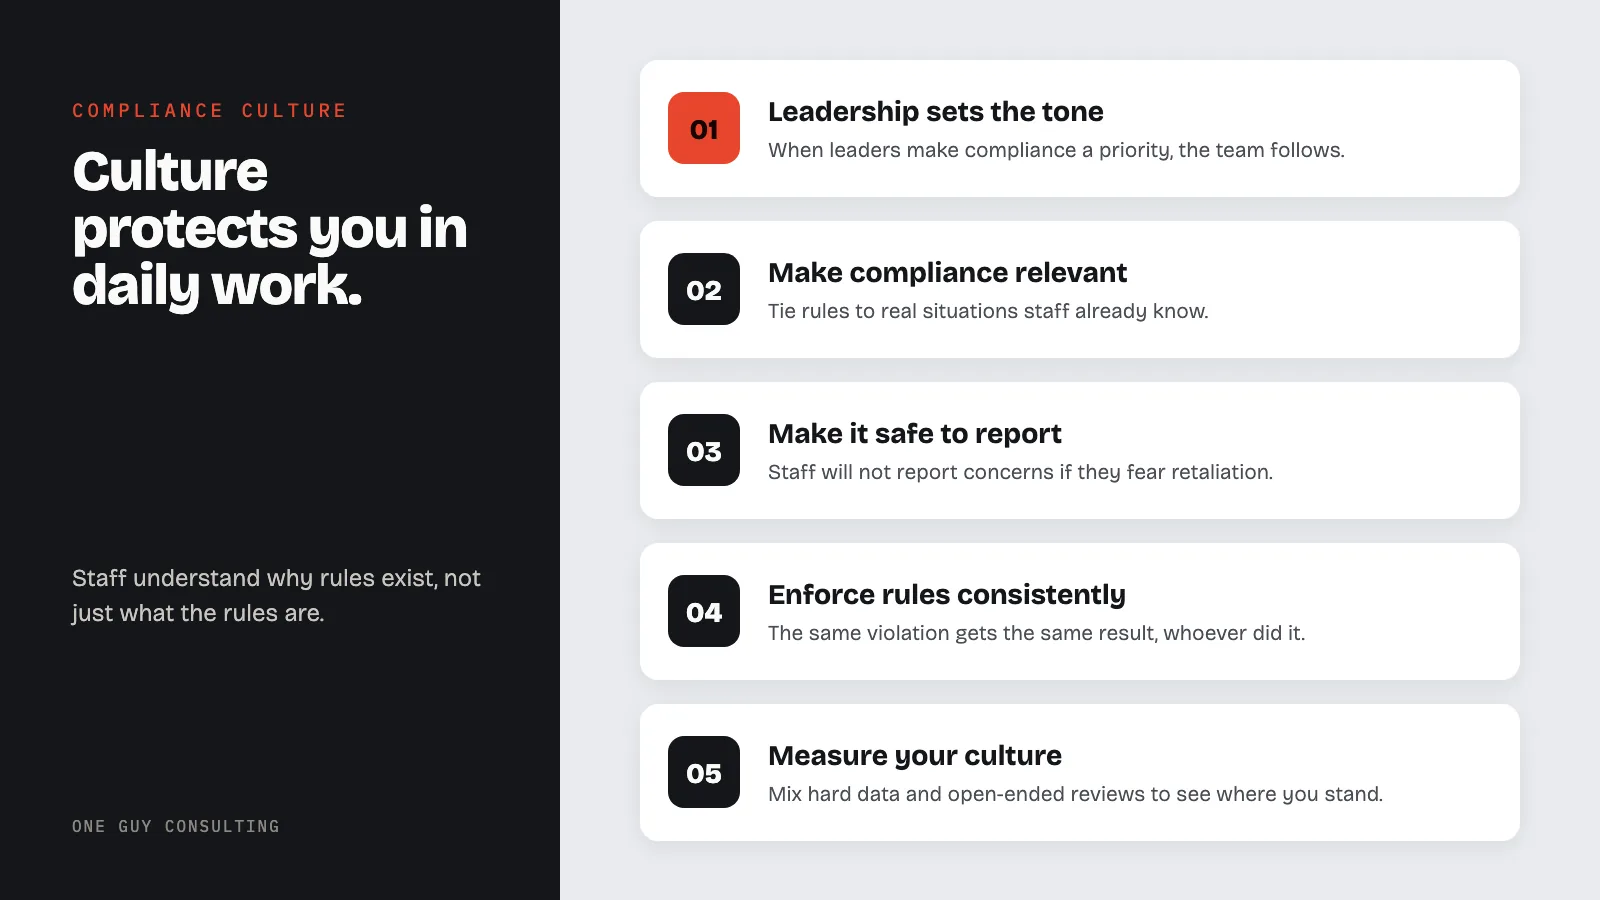
Direct answer: A healthcare compliance culture means staff understand WHY compliance rules exist, not just WHAT the rules are. It requires leadership modeling compliant behavior, regular contextual training (not just annual checkbox sessions), protected reporting channels where staff can raise concerns without retaliation, and measurement systems that track understanding rather than just policy existence.
A strong culture helps staff catch problems early and report them quickly, instead of hiding them.
Compliance vs. Compliance Culture
| Compliance | Compliance Culture |
|---|---|
| Written policies exist | Staff can explain why each policy matters |
| Training is completed annually | Training uses real scenarios relevant to each role |
| Incident reporting form exists | Staff report incidents without fear of retaliation |
| Compliance officer is designated | Every manager treats compliance as part of their job |
| BAAs (business associate agreements, the contracts where vendors promise to protect patient data) are signed with vendors | Staff know what a BAA is and why it matters |
| Rules are enforced when violations are caught | Rules are enforced consistently regardless of who is involved |
| Measures policy existence | Measures policy understanding and behavior change |
What It Is and Why It Matters
A compliance culture is the gap between a team that follows rules because it must and one that protects patient data because it cares. The difference is belief. Policies and procedures matter. But they only work when people are truly committed to the mission they serve.
Teams that see compliance as rules forced on them often fall short. Teams that make it part of who they are do better. Building a compliance culture is not a one-time project. It is an ongoing effort. It starts with leadership and runs through every unit. It shapes how every staff member thinks about daily work.
When compliance is part of who you are, your team gets better at stopping threats. Those are exactly the threats HIPAA was built to address. This guide gives you a practical framework for building, keeping, and measuring a compliance culture. It goes beyond bare minimums.
What Compliance Culture Really Means
Beyond Policies and Procedures
Every healthcare team has policies. Many have thick manuals that sit on shelves or in shared drives, rarely read and poorly grasped. A compliance culture is not about the quantity or quality of your written records. It is about the gap between what those records say and what people actually do.
A true compliance culture shows these traits:
- Employees understand why rules exist, not just what the rules are
- Reporting is encouraged and reporters are protected, not punished
- Leadership models the right behavior visibly and consistently
- Compliance is integrated into performance reviews and daily operations
- Mistakes are learning opportunities, not just grounds for punishment
- People speak up when they see something wrong, because they trust the system
A strong compliance culture helps a team catch issues sooner and fix them faster. It also leaves a record of real effort, not just paperwork. That record matters if the HHS Office for Civil Rights (OCR) ever investigates. OCR is the federal office that enforces HIPAA.
The Cost of a Weak Compliance Culture
When compliance is an afterthought, the results go far beyond fines. Teams with weak cultures face a chain of problems that build over time.
- Higher breach rates: Staff who do not understand or care about compliance make more errors. More errors mean more breaches.
- Delayed reporting: Fear of blame causes people to hide errors. They report fewer incidents as a result.
- More turnover: Ethical staff leave teams where they see compliance ignored
- Regulatory scrutiny: OCR gives harsher fines when an investigation finds willful neglect, which means knowingly ignoring the rules. If that neglect is not fixed within 30 days, the minimum penalty is $73,011 per violation. That figure comes from the 2025 inflation-adjusted amounts in 45 CFR 102.3.
- Reputation damage: Patients and partners lose trust when compliance fails in public
- Financial exposure: Civil money penalties (fines from OCR) can reach $2,190,294 per calendar year for identical violations, meaning the same violation repeated. That is the 2025 inflation-adjusted cap in 45 CFR 102.3. The risk is real.
Leadership and governance
Governance starts with named owners. HIPAA requires a covered entity to designate a privacy official (45 CFR 164.530(a)(1)) and every covered entity and business associate to identify a security official (45 CFR 164.308(a)(2)). In a small practice one person can hold both roles, in writing. For the wider structure (a compliance committee, reporting lines, auditing), the HHS Office of Inspector General publishes its General Compliance Program Guidance, a voluntary reference guide for the health care compliance community.
Setting the Tone at the Top
Compliance culture starts in the executive suite. When leaders treat compliance as a top priority, that attitude flows through the team. When leaders cut corners, everyone notices, and many follow suit.
Leadership actions that build compliance culture:
- Allocate enough resources: Budget for compliance staff, tools, and training
- Participate in training: Executives who do the same HIPAA training as front-line staff send a strong message. It shows compliance applies to everyone.
- Discuss compliance in leadership meetings: Add compliance metrics to your leadership dashboards
- Respond visibly to incidents: How leaders handle breaches sets the tone. Everyone is watching.
- Reward compliance excellence: Recognize units and people who model strong compliance
Middle Management as Culture Carriers
Executives set the direction. But middle managers determine whether it takes root. Supervisors and team leads shape culture daily. Their behavior drives how front-line staff approach compliance.
Empowering middle managers:
- Train managers directly on their compliance leadership duties
- Give managers power to address compliance issues in their teams
- Include compliance metrics in manager performance reviews
- Give managers regular compliance updates and talking points
- Create forums for managers to share challenges and fixes
Staff training and routines
Training is where culture becomes behavior, and HIPAA sets the floor. The Privacy Rule states:
"A covered entity must train all members of its workforce on the policies and procedures with respect to protected health information required by this subpart and subpart D of this part, as necessary and appropriate for the members of the workforce to carry out their functions within the covered entity."
(HHS, 45 CFR 164.530(b)(1))
New workforce members must be trained "within a reasonable period of time" after joining (164.530(b)(2)(i)(B)), and the Security Rule adds a security awareness and training program for the whole workforce, including management (164.308(a)(5)(i)). NIST SP 800-50 Rev. 1, Building a Cybersecurity and Privacy Learning Program, shows how to plan it.
- Onboarding: HIPAA training before a new hire touches patient records.
- Annual refresher: role-specific scenarios, with a short knowledge check.
- Five-minute huddles: one real example per month (a misdirected fax, a phishing email).
- Phishing simulations: track click rates by team over time.
- Training log: who, when, and what was covered, kept six years.
Communication Strategies That Work
Making Compliance Relevant
The biggest enemy of compliance culture is irrelevance. When training feels cut off from daily work, people tune out. Good compliance messages tie rules to real situations staff know.
Key principles:
- Tell stories, not rules: Share real examples of breaches. Show their impact on patients, not just legal citations.
- Use plain language: Turn legal rules into clear, plain guidance
- Be specific to roles: A nurse needs different compliance reminders than a billing specialist. Role-based messages land better.
- Keep frequency without fatigue: Short, frequent messages beat big info dumps
- Create two-way channels: Compliance messages should invite questions, not just push instructions
Multi-Channel Outreach
People take in info in different ways. A good strategy uses multiple touchpoints to drive key messages home.
- Monthly compliance newsletters: Brief updates on rule changes and reminders
- Departmental huddles: Five-minute compliance topics in team meetings
- Intranet portal: A central hub with searchable policies, FAQs, and contact info
- Visual reminders: Posters, screen savers, and badge cards with key compliance reminders
- Email alerts: Quick alerts about threats, policy changes, or trends
- Annual compliance week: A yearly event with activities, speakers, and awards
Employee Engagement and Reporting
Building Psychological Safety
Staff will not report concerns if they fear retaliation, meaning being punished for speaking up. Psychological safety is the base of a good reporting culture. It means people feel safe to speak up without being blamed. Your team must believe that raising a concern will get support. That holds even when the concern is about their own mistake.
Creating psychological safety around compliance:
- Set up clear non-retaliation policies and communicate them often
- Respond well to reports. Focus on fixing the system, not blaming people.
- Follow up with reporters to confirm their concern was heard. Let them know what happened next.
- Celebrate reporting as a positive asset to team safety
- Address retaliation swiftly when it occurs, showing that protection is real
Effective Reporting Tools
Multiple channels give every staff member a way to speak up. Not everyone will walk into the compliance officer's office. They should not have to.
Useful reporting channels:
- Direct supervisor reporting: The most natural first step for many employees
- Compliance officer or hotline: Direct access to the compliance team for sensitive issues
- Anonymous reporting system: Web or phone-based anonymous reporting for concerns about retaliation
- Online incident reporting forms: Digital forms that guide reporters through the info needed
- Peer reporting programs: Trained compliance champions in each unit who can escalate concerns
For guidance on the role of the compliance officer in managing these channels, see the article on HIPAA compliance officer duties.
Accountability Frameworks
Consistent Enforcement
A compliance culture cannot survive uneven enforcement. When violations are excused for senior leaders, the message is clear. Compliance is optional. At all levels, enforcement must be consistent.
Building accountability:
- Apply sanctions uniformly: The same violation gets the same result. It does not matter who did it.
- Document every action: Keep a paper trail showing consistent enforcement
- Conduct root cause analysis: Find out what caused the violation. Was it personal behavior, a system flaw, or a training gap?
- Separate honest mistakes from negligence: Use a just culture framework. It splits error, at-risk behavior, and reckless conduct.
- Track corrective actions: Check whether corrective steps prevent recurrence
Integrating Compliance into Performance Reviews
Compliance should not live apart from the rest of employee performance. When compliance metrics appear in reviews, staff get the message. Compliance matters as much as output and quality.
Integration strategies:
- Add compliance goals to annual performance reviews
- Include compliance in competency assessments for all roles
- Factor training scores into performance reviews
- Factor compliance excellence into promotion decisions
- Address compliance gaps with improvement plans
Recognition Programs
Rewarding Compliance Excellence
Most teams punish failures fast but reward success slowly. This sends the message that compliance is a trap, not a goal. Recognition programs shift that balance.
Effective recognition approaches:
- Champion awards: Monthly or quarterly awards for strong compliance behavior
- Department compliance scorecard: Public reporting of unit metrics with awards for top performers
- Reporting recognition: Acknowledge staff who self-report quickly. It shows that reporting is valued.
- Training awards: Recognize people or teams with the best training scores
- Compliance innovation awards: Celebrate staff who suggest fixes that strengthen compliance
Policies, BAAs, and documentation
Written policies are the agreement a culture is measured against. HIPAA requires them (164.530(i)(1) and 164.316(b)(1)), and requires a sanctions policy applied to workforce members who do not follow them (164.530(e)(1); 164.308(a)(1)(ii)(C)).
- Policy templates: privacy, security, breach response, sanctions, and acceptable use, each with an owner and a review date.
- BAAs (Business Associate Agreements, the contracts where vendors promise to protect patient data): one for every vendor that touches PHI, signed before access (164.504(e)).
- Risk assessment (a documented review of the risks to electronic PHI): the base every policy is written from (164.308(a)(1)(ii)(A)).
- Documentation: policies, training records and assessments kept for six years (164.316(b)(2)(i)).
Tools and Vendor Checklist
- A policy library with version history and staff acknowledgments.
- A training platform that records completion and scores.
- A vendor list with BAA status and renewal dates.
- An incident log that anyone on staff can add to.
- Encryption (scrambling data so only key holders can read it) on laptops and backups.
Monitoring, audits and continuous improvement
HIPAA builds monitoring in: regular review of "audit logs, access reports, and security incident tracking reports" (164.308(a)(1)(ii)(D)) and a periodic evaluation of the security program (164.308(a)(8)). The culture measures below sit on top of those.
Quantitative Indicators
Culture is hard to measure, but you can do it. A mix of hard data and open-ended reviews shows you where your culture stands.
Key metrics to track:
- Training completion rates and scores: Trend data on engagement levels over time
- Report volume: A rising trend shows growing awareness and willingness to report
- Time to report incidents: Shorter times mean people feel safe raising concerns
- Audit findings: Fewer findings over time show improving compliance behavior
- Phishing simulation results: Falling click rates show growing security awareness
- Sanctions data: Trend patterns by violation type, unit, and severity
- Employee survey scores: Ask how staff view compliance. Ask about their confidence in it.
Open-Ended Review
Numbers give the outline. Open-ended methods fill in what data misses.
- Annual compliance culture survey: Ask about compliance commitment. Ask about leader behavior. These questions reveal a lot.
- Focus groups: Group talks about compliance challenges and culture across units
- Exit interviews: Staff who leave often share candid views on team culture
- Walk-through observations: Direct observation of behavior in clinical and admin areas
- Compliance committee feedback: Regular input from committee members on cultural trends
Common Compliance Culture Mistakes
These are the most common failures that prevent a compliance culture from taking root. Each one creates the appearance of compliance without the substance:
- Checkbox training. Annual training that consists of reading a slide deck and clicking "acknowledge." Staff often retain little. Under 45 CFR 164.308(a)(5), the Security Rule requires a security awareness and training program. It must cover all workforce members, including management. A slide deck no one remembers does little to meet that goal. Effective training uses role-specific scenarios, real breach examples, and tests understanding rather than attendance.
- Leadership exemptions. When executives or physicians skip training, ignore policies, or receive lighter enforcement for violations, the entire organization receives a clear message: compliance is optional for people who matter. This is one of the fastest ways to destroy a compliance culture.
- Punishing reporters. If staff who report incidents face retaliation (formal or informal), reporting stops. Unreported incidents become undetected breaches. Under the HIPAA Privacy Rule, covered entities must not retaliate against individuals who file complaints (45 CFR 164.530(g)). Covered entities are health plans, health care clearinghouses, and health care providers who send claims or other standard transactions electronically.
- Measuring policy existence instead of understanding. Having 47 written policies means nothing if staff cannot explain the three most important ones. Effective measurement asks: "Can a front-desk employee explain why they should not email PHI (protected health information, such as patient records) to a personal account?" not "Does a policy about email exist?"
- Treating compliance as a department. When compliance belongs solely to the compliance officer, everyone else treats it as someone else's job. Compliance must be embedded in every department, every manager's responsibilities, and every performance review.
Measuring Compliance Culture: Specific Metrics
Abstract culture goals are not actionable. Track these specific metrics quarterly to measure whether your compliance culture is strengthening or eroding:
- Anonymous survey scores. Ask staff: "Do you feel safe reporting a compliance concern to your supervisor?" and "Can you describe what PHI means without looking it up?" Track scores over time. Declining scores are an early warning.
- Incident reporting trends. Increasing report volume usually indicates growing awareness and psychological safety, not worsening compliance. A sudden drop in reporting is a red flag.
- Training completion rates with comprehension scores. Track not just who completed training, but how they scored on scenario-based questions. Aim for real comprehension, not just 100% completion.
- Time-to-report metrics. Measure the average time between when an incident occurs and when it is reported. Shorter times indicate stronger trust in the reporting system. Under the Breach Notification Rule, you must notify affected patients without unreasonable delay. The outer limit is 60 calendar days after a breach is discovered (45 CFR 164.404(b)). A breach counts as discovered once any workforce member knows about it, other than the person who caused it (45 CFR 164.404(a)(2)). So internal reporting should happen within hours.
- Phishing simulation click rates. Run monthly simulated phishing emails. Track click rates by department. Declining rates over time show growing security awareness.
Overcoming Resistance to Change
Common Sources of Resistance
Building a compliance culture means hitting resistance. Knowing the source helps you address it well, not just demand more compliance.
Typical resistance patterns:
- "We've always done it this way": Long-serving staff often see new rules as needless change. This is one of the most common resistance patterns.
- "Compliance slows us down": Some clinicians see compliance as a block. They feel it slows down their work.
- "Nothing bad has happened yet": Complacency from the lack of visible results
- "That's the compliance department's job": Staff who see compliance as someone else's job
- "Leadership doesn't really care": Cynicism from uneven enforcement or too few resources
Strategies for Overcoming Resistance
- Address the why before the what: Help people see that compliance protects patients. It also protects their own careers.
- Involve resisters in solutions: Ask skeptics to help design procedures. The procedures should be compliant and fast.
- Show leadership commitment: Visible actions speak louder than compliance memos
- Start with quick wins: Target areas where compliance gains also cut friction
- Share success stories: Share examples where compliance stopped harm
- Be patient: Culture change takes years, not months. Celebrate small wins.
How to start and next steps checklist
How to Start
- Leadership commitment: the owner or administrator names the privacy and security officials in writing.
- Written policies: adopt or update the core set and have every staff member acknowledge them.
- Regular staff training: onboarding plus an annual refresher, logged.
- Monitoring: a quarterly review of incident reports, audit logs and training scores.
Next Steps Checklist
- Privacy and security officials named in writing.
- Risk assessment current and a remediation plan in progress.
- Policies acknowledged by every workforce member.
- Training log complete for the last 12 months.
- BAA on file for every vendor that touches PHI.
- Anonymous reporting channel announced and tested.
- Quarterly culture metrics reviewed by leadership.
Case Example
Anonymized, from One Guy Consulting's case studies: a health group with more than 100 offices had money, backing at the top and systems, but take-up of its compliance program swung widely from office to office. Reading the activity data and reaching out office by office, person to person, lifted take-up by about 17%. Read case 03.
FAQ
What is a healthcare compliance culture?
A workplace where HIPAA and security practices are embedded in daily operations.
Why build one?
To ensure consistent care workflows and protect patient data across the practice.
How do we start?
Start with leadership commitment, written policies, regular staff training, and monitoring.
How can One Guy Consulting help?
One Guy Consulting provides HIPAA compliance and cybersecurity SaaS for practices to manage policies and training.
How One Guy Consulting Can Help
Building a compliance culture is one of the most important investments a healthcare team can make. Policies protect you on paper. Culture protects you in daily work. The teams that survive audits and keep patient trust share one trait. Compliance is woven into daily work.
Start with leadership commitment. Build channels that make compliance clear and easy to use. Create fair, consistent rules for accountability. Recognize the people who model the right behavior. Measure progress and adjust based on what you find.
One Guy Consulting works with healthcare teams to build compliance cultures that go beyond bare minimums. The goal is a team where doing the right thing is just how things are done. Start with a gap analysis to begin building your compliance culture, or read the complete HIPAA compliance guide for the full regulatory picture. One Guy Consulting's compliance training and the Full-Scope plan ($1,300 a year, or $120 a month, flat rate per location) cover the policies, training and BAAs above.
Key point: The Security Rule requires a security awareness and training program under 45 CFR 164.308(a)(5). It covers all workforce members, including management. But a compliance culture goes beyond training. It means building compliance into hiring, onboarding, performance reviews, and daily operations.
Sources
- HHS Office for Civil Rights
- HHS OIG: General Compliance Program Guidance
- NIST SP 800-50 Rev. 1: Building a Cybersecurity and Privacy Learning Program
- CMS: Are You a Covered Entity?
- 45 CFR 164.530: Privacy Rule administrative requirements (training, sanctions, policies)
- 45 CFR 164.308: Administrative Safeguards
- HHS OCR Enforcement Actions
Compliance Program Resources
Try three One Guy Consulting 3D staff training courses free →